


MediaTek Chip Vulnerability Exposes Android Phones Patch Issued in January
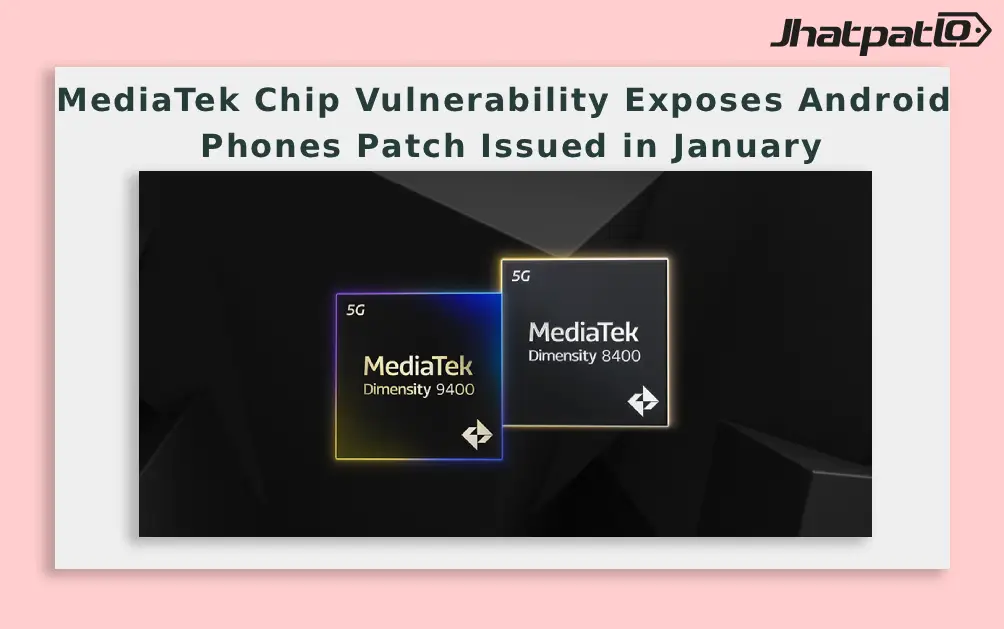
Researchers at Ledger Donjon say a vulnerability in MediaTek's Dimensity and Helio chipsets could allow attackers to access Android smartphones within minutes of connection by targeting the Trustonic TEE, a trusted execution environment that protects sensitive user data. The flaw, if present across affected devices, could let intruders reach a phone's security PIN, decrypted storage, and seed phrases for popular cryptocurrency wallets. Ledger's post on X cites testing on the CMF Phone 1 powered by a Dimensity 7300, with security access achieved 45 seconds after the device was plugged into a computer. MediaTek has said a patch was issued to device makers in January, but it remains unclear whether all affected devices have been updated. OEMs have not publicly acknowledged the vulnerability as of publication.
The vulnerability is described as stemming from the Trustonic TEE used by MediaTek's Dimensity and Helio series. The research group reported that it could breach the phone's protection and access the security PIN, decrypt storage, and extract seed phrases used by popular software wallets for cryptocurrency verification and account recovery. The findings, presented by Ledger Donjon, heighten concerns about the security of Android devices powered by MediaTek chips when the trusted execution environment is compromised.
Discovery and Affected Devices
In a post on X, Ledger Donjon researchers say they tested the vulnerability on the CMF Phone 1, a device equipped with the Dimensity 7300 chipset. They report that the breach occurred within 45 seconds of the device being connected to a computer, and that the attacker could recover sensitive data without turning on the phone in some scenarios. The group notes the issue appears to stem from the Trustonic TEE used on MediaTek's Dimensity and Helio lines, which is intended to protect sensitive data on Android handsets.
Patch Status and Security Landscape
As of publication, OEMs have not publicly acknowledged the vulnerability. MediaTek told Android Authority that it issued a patch for the vulnerability to device makers as early as January; it is not known whether all affected devices have received the patch. Ledger's claims imply a potentially wide impact, with millions of Android phones powered by MediaTek chips possibly at risk. By contrast, smartphones from other brands, including Google and Apple, and devices built on Snapdragon chips, are described as having dedicated security chips that protect user information.
Technical Details
- Chipsets involved: MediaTek Dimensity and Helio series
- Security environment: Trustonic TEE
- Test device cited: CMF Phone 1
- Chip tested: Dimensity 7300
- Time to breach observed: 45 seconds after connection
- Data potentially exposed: security PIN, decrypted storage, seed phrases for cryptocurrency wallets
- Phone state during breach: data could be recovered even if the phone was not turned on
- Patch status: patch issued to device makers in January; impact scope unclear
- OEM response: no public acknowledgment fromOEMs as of publication
- Security landscape contrast: other brands are said to use dedicated security chips
No additional details are provided beyond the claims and the patch note from MediaTek. The situation remains under observation as OEMs, and independent researchers await further verification and potential updates.
Related Products


Digital Lutera Android Toolkit Hijacks UPI Accounts, NPCI Responds
Digital Lutera Android Toolkit Hijacks UPI Accounts, NPCI Responds The government has pressed ahead with a SIM-binding mandate for messaging and financial platforms, saying the move connects services like messaging apps and UPI platforms to the user’s primary device. DoT officials describe the...
HMD Thunder Pro Leak Reveals OLED Display and 6,000mAh Battery
HMD Thunder Pro Leak Points to a Utility First Midrange Strategy HMD Thunder Pro Leak Reveals ahead of launch, along with renders and a detailed specifications sheet that point to a battery-focused midrange smartphone. The leaked information suggests a 6.67-inch OLED display, a 6,000mAh battery,...
Alleged Honor 600e Appears on Geekbench With Android 16 and 8GB RAM
Honor 600e Listing Surfaces on Geekbench An alleged Honor 600e has appeared on Geekbench with model code LNA-NX3, giving an early look at its key specs before any official word from Honor, as Honor 600e Pops Up on Geekbench. The listing shows the device running Android 16, paired with MediaTe...
Honor 600 Lite Geekbench Listing Confirms Dimensity 7100
Honor 600 Lite Geekbench Listing Confirms Dimensity 7100 Honor's next budget-to-midrange handset, the 600 Lite, has surfaced in Geekbench benchmarks, offering early hardware details ahead of an official debut. The listing identifies an unreleased device with the model number LNA-NX1, beli...
DarkSword iOS Toolkit Goes Public on GitHub Lowering Exploit Barriers
DarkSword, an iOS full chain spyware toolkit, has been published publicly on GitHub, potentially lowering the barrier for attackers to exploit vulnerabilities on older iPhone devices. iVerify researchers said the updated version was uploaded to GitHub, making it easier to access and deploy...
Samsung Galaxy M47 Leak Shows Snapdragon 6 Gen 3 and Android 16
Samsung’s Galaxy M47 has appeared on Geekbench with a Snapdragon 6 Gen 3 chipset, 8GB RAM, Android 16 and One UI 8, according to the leak. The benchmark listing is the clearest early sign yet of the phone’s hardware direction before launch. Galaxy M47 Leak Confirms Samsung’s Hardware Directio...